Teramis Use Cases
Purpose-Built CUI Discovery for Real-World Risk
and Compliance Scenarios
CUI Spillage Management
Monitor and validate your CUI footprint over time.
CUI isn’t static. Files move, teams change, and systems evolve. Teramis provides automated scanning to detect CUI spillage, helping organizations identify data that appears outside approved boundaries.
DFARS requires you to safeguard CUI and control where it flows.
- Do you know where your CUI is?
- Do you know who uses CUI?
- Did you move your CUI into your enclave?
Do not rely on assumptions about whether CUI has been moved into the approved enclave or whether a user has accidentally spilled it. Find your CUI today.
CUI Scoping & Self-Assessment Preparation
Define your CUI boundary before a DoD reviewer or prime contractor asks you to prove it.
Before implementing security controls or designing a secure enclave, organizations need to accurately identify where CUI resides across legacy file shares, endpoints, and cloud environments. Scoping lays the groundwork for compliant system boundaries and risk management.
A properly sized CUI scope can reduce compliance costs, eliminate unnecessary security control implementations, and ensure you're not paying to protect data that isn't actually CUI.
Post-Breach CUI Reporting
Identification for Accurate Reporting
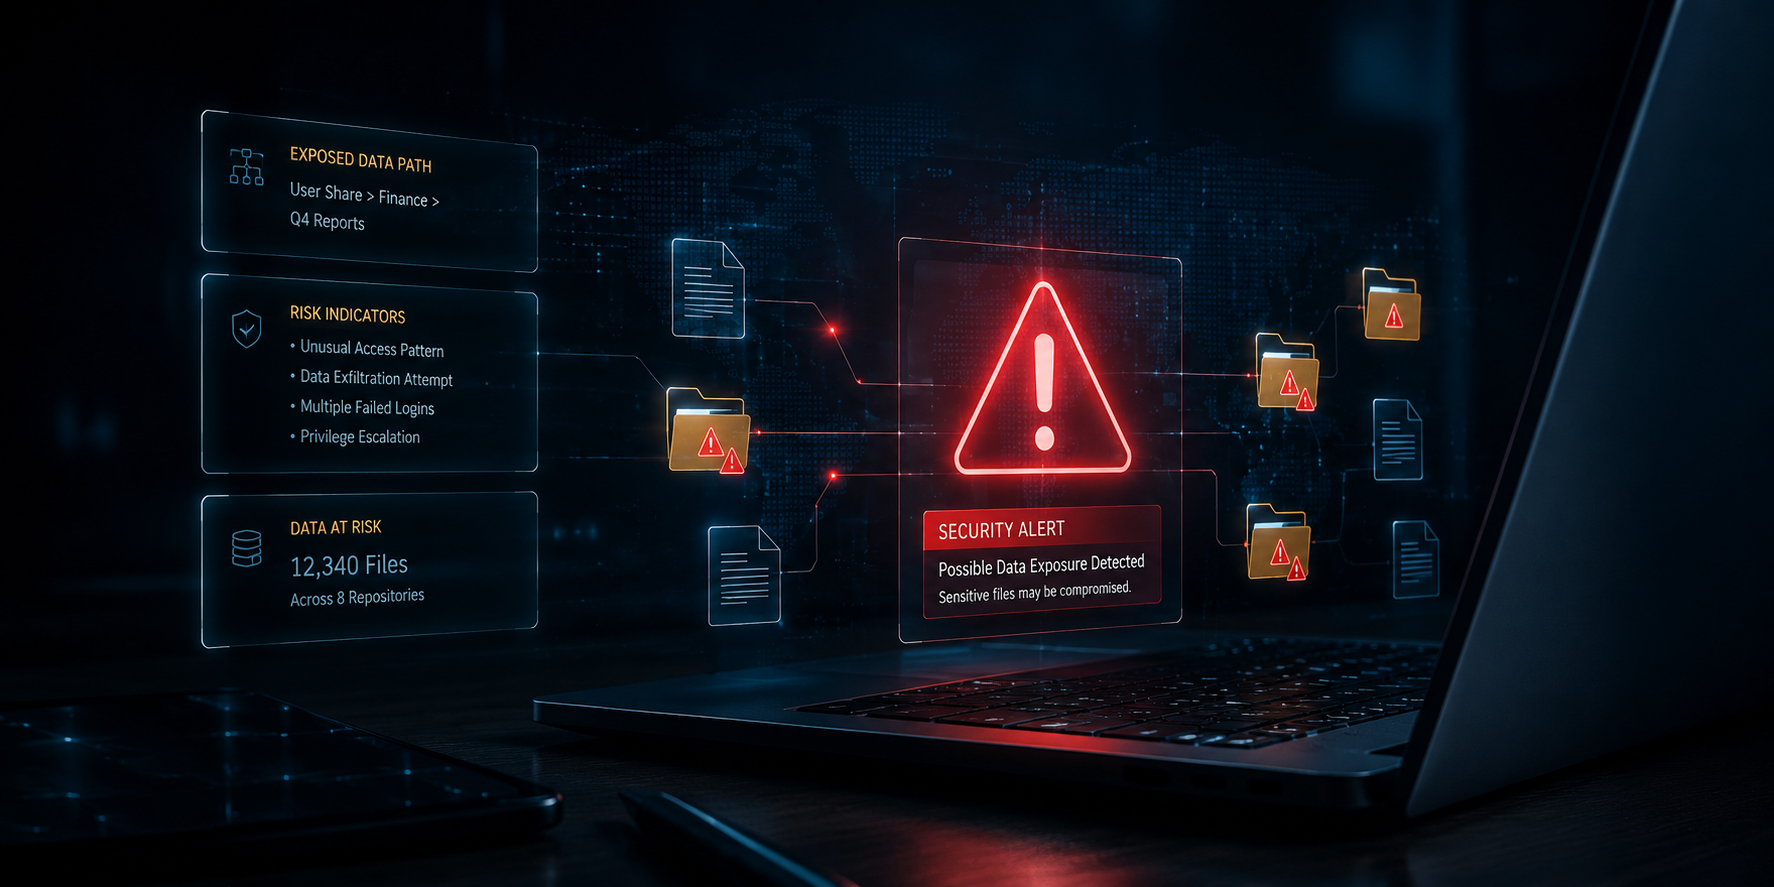
Following a security incident or suspected data spill, teams must quickly determine whether or not CUI may have been impacted for DFARS Breach Reporting Requirements.
Teramis accelerates this process by scanning affected systems and repositories to precisely identify if CUI exists on compromised systems. Don't inadvertently report a CUI breach because of a false positive.