Find
Discover CUI across approved Microsoft 365 environments, file systems, email, endpoints, CAD files, PDFs, scanned documents, archives, engineering repositories, and other supported sources.
THE TERAMIS PLATFORM
Teramis is a CUI discovery platform that helps Defense Industrial Base organizations find Controlled Unclassified Information, validate their documented boundary, and monitor for changes over time.
See what exists across your approved data environments and give your compliance, security, and advisory teams evidence they can act on.
Purpose-built CUI discovery with scanning and analysis performed within the customer environment.
WHY DISCOVERY COMES FIRST
Policies, interviews, asset inventories, and diagrams describe where CUI is expected to reside. They do not always show where it exists today.
CUI can appear in email attachments, shared drives, project folders, endpoints, engineering repositories, scanned documents, archives, and other locations that are difficult to assess through assumptions alone.
Teramis provides the discovery and validation layer needed to compare your documented boundary with the environment you actually have.
You cannot defend what you cannot prove.
Trusted by leading companies
HOW TERAMIS WORKS
Teramis examines approved data sources to identify potential Controlled Unclassified Information, validate findings, document the CUI footprint, and monitor for changes over time.
This gives compliance, security, IT, and advisory teams evidence to support CMMC scoping and boundary decisions.
Discover CUI across approved Microsoft 365 environments, file systems, email, endpoints, CAD files, PDFs, scanned documents, archives, engineering repositories, and other supported sources.
Validate findings and produce evidence that helps executives, CMMC advisors, compliance teams, and assessors understand whether the documented boundary matches the actual environment.
Run recurring scans to identify new CUI, movement, spillage, and boundary drift before the next assessment, annual affirmation, prime contractor request, or internal review.
WHAT TERAMIS EXAMINES
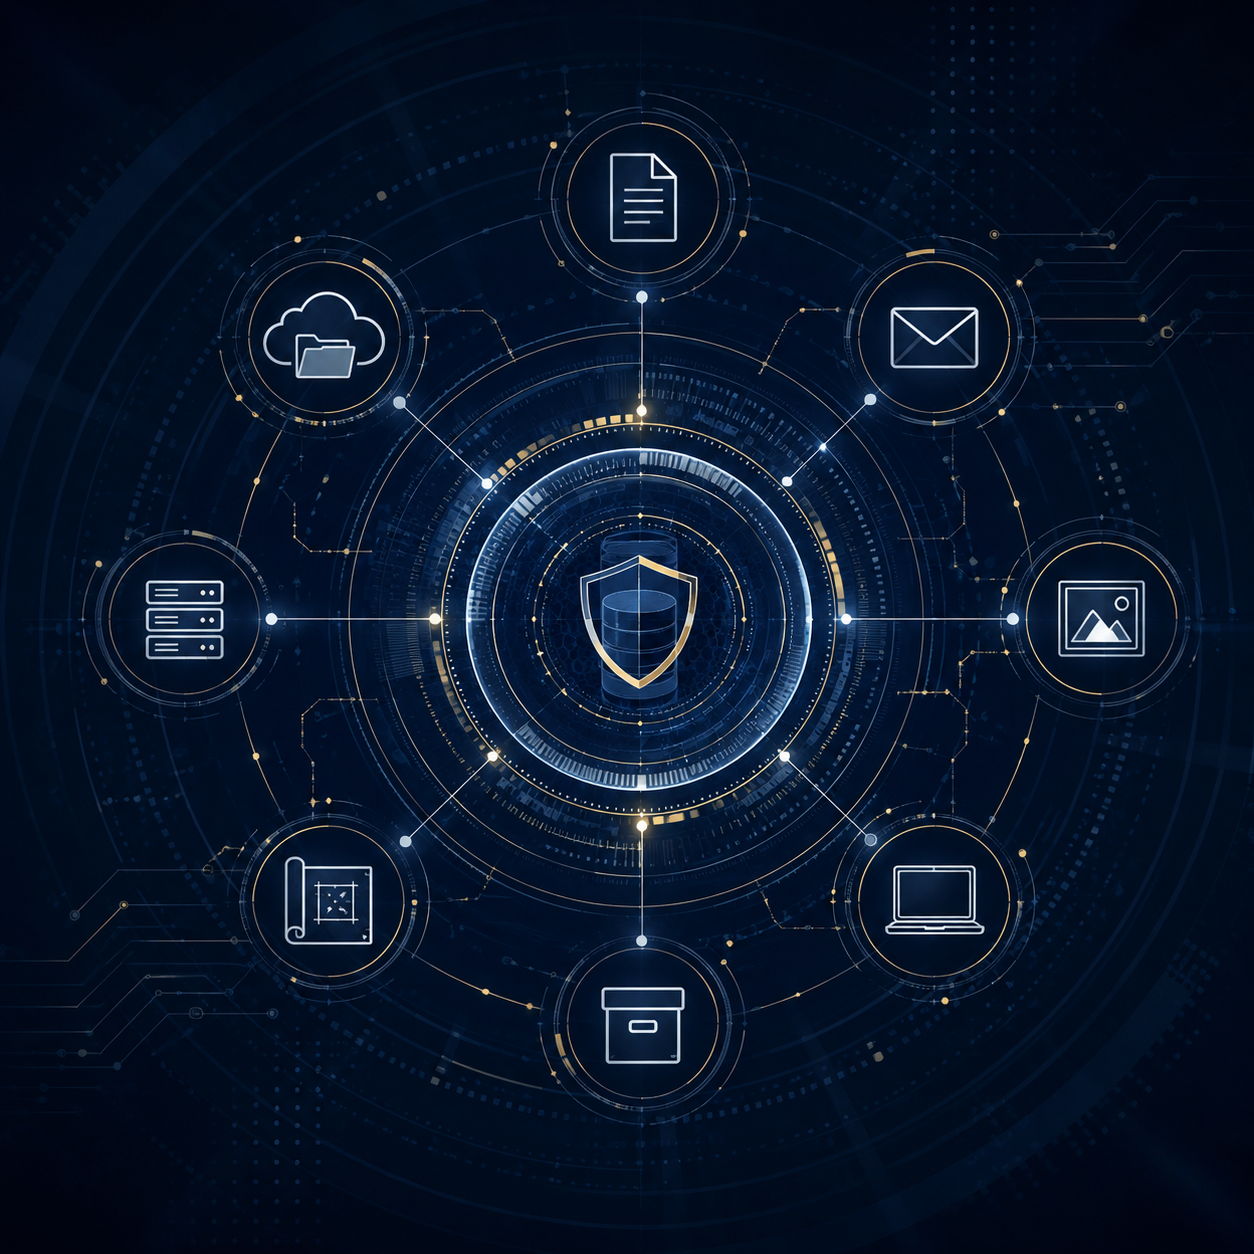
Teramis is designed for the mixed environments common across the Defense Industrial Base, including:
Microsoft 365 repositories, including SharePoint, OneDrive, and Exchange
Network file shares, endpoints, legacy storage, and distributed repositories
Project and engineering folders
PDFs, Office documents, images, scanned documents, email files, archives, and other supported structured and unstructured content
SharePoint
OneDrive
Exchange
Supported Microsoft 365 repositories
Network file shares
Local and distributed endpoints
Legacy repositories
Project and engineering folders
CAD and engineering files
PDFs
Images and scanned documents
Email and attachments
Archives
Structured and unstructured files
BETTER TOGETHER WITH YOUR EXISTING STACK
Teramis is an evidence layer, not a replacement for your security, governance, compliance, or assessment systems.Teramis helps identify and validate where CUI exists. Existing tools and authorized teams can then apply labels, manage access, enforce policy, organize compliance work, or determine next steps.
Use labels and compliance workflows with stronger CUI discovery evidence.
Support access governance with clearer visibility into where CUI exists.
Strengthen enforcement strategies by starting with better CUI ground truth.
Connect documentation, control evidence, and boundary decisions to the actual CUI footprint.
Find CUI across approved repositories, platforms, endpoints, and supported file types.
Organize file-level findings, repository details, exceptions, and validation output to support CMMC scoping and boundary decisions.
Track changes over time and surface new findings, potential spillage, and movement outside approved locations.
Understand deployment options, supported data sources, distributed environments, and complex file types.
Teramis provides evidence your compliance, security, and advisory teams can use to understand what was found, where it was found, and what may require further review.
Review individual files identified during discovery so your team can evaluate findings at the level where CUI decisions are made.
Understand where identified CUI resides across the repositories, systems, and locations included in the engagement.
Surface findings outside expected or approved locations so the responsible team can determine the appropriate next action.
Review validation information that helps distinguish meaningful findings from noise and supports evidence-based decisions.
Compare results between scans to identify newly introduced CUI, movement, and changes in the known CUI footprint.
Give compliance, security, and advisory teams findings they can use when evaluating CMMC scope and preparing for assessment activities.
The result is a clearer record of what was found, where it was found, and what may require further review.
Teramis is designed to support discovery and evidence workflows while keeping responsibility for remediation and security decisions with the customer or authorized partner.
DEPLOYMENT AND EXECUTION
Teramis is designed to support organizations that need control over how sensitive data is examined. Scanning and analysis can be configured around the customer’s approved environment, including distributed and hybrid deployments.
PRODUCT BOUNDARY
Teramis identifies, validates, reports, and monitors CUI. It does not move, tag, alter, encrypt, remediate, or delete discovered data.
Teramis does not certify an organization or guarantee an assessment outcome. It produces the evidence; your team or your partner decides what to do with it.
REQUEST A DEMO
Discover how Teramis helps your organization find CUI, validate its boundary, and maintain visibility as the environment changes.